Non-Human Identity Management for MCP Agents
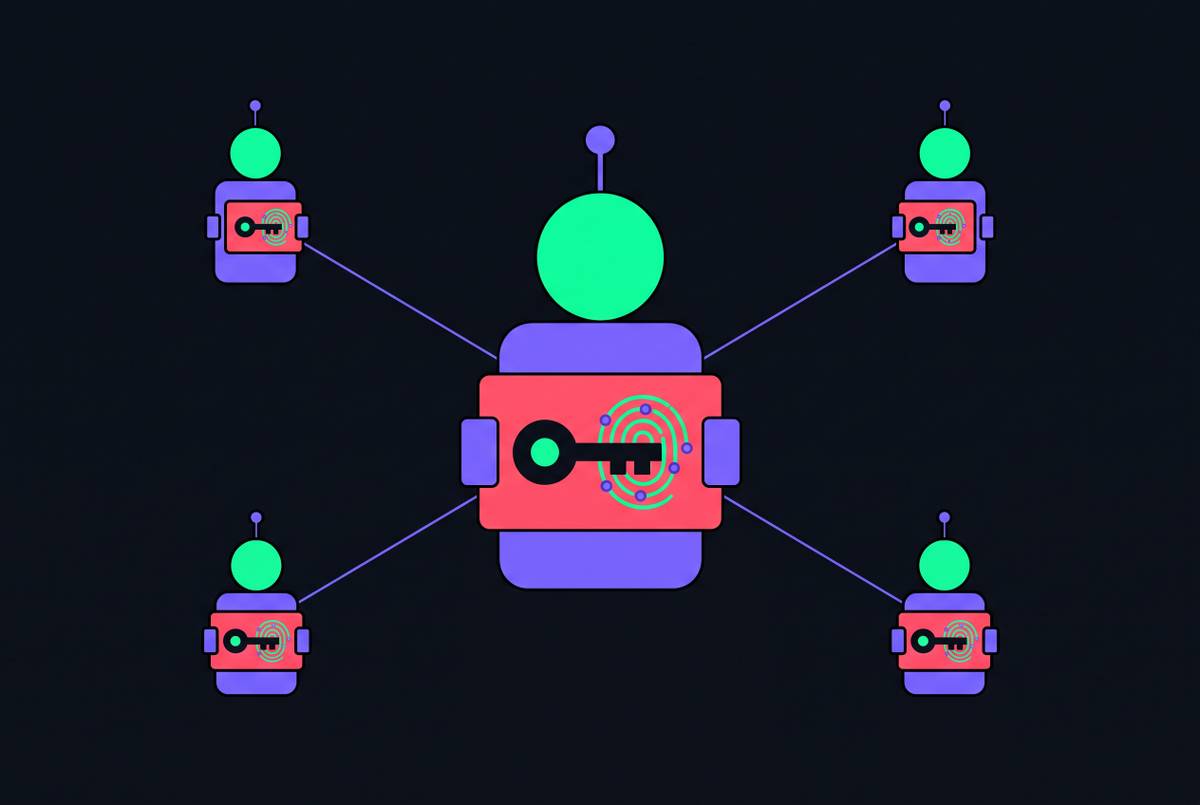
Agent actions need tied identities, not borrowed credentials.
Colin Reyes
Slack agents inherit enterprise system access with no built-in approval controls.
Agent actions need tied identities, not borrowed credentials.
Banks deploying AI agents now must map existing compliance rules to MCP's novel security risks.
New monitoring platforms fill a security gap that existed tools cannot see.
enterprises overlook authorization because the protocol leaves security entirely to implementers.
Enterprises must build RBAC into MCP deployments to meet compliance requirements.
MCP's trust boundaries collapse in production, enabling unauthorized tool calls at scale.
Gateways enforce security that MCP left unbuilt; platforms add catalog and identity to the equation.
Adversarial prompting exploits blind spots in principle-based refusal at scale.
Four boolean hints preview tool behavior, but only if you trust the server supplying them.
Platform engineering must evolve to govern AI agents with the same rigor it uses for humans.
Enterprises are deploying AI agents faster than security frameworks can govern them.