security platforms that monitor agent context drift during live MCP sessions
Most security tools check MCP sessions once, missing the attacks that happen during live execution.
Ayana Brennan
Correspondent
Ayana Brennan covers agent security and agentic ai foundations for LetterMCP.
11 stories
Most security tools check MCP sessions once, missing the attacks that happen during live execution.
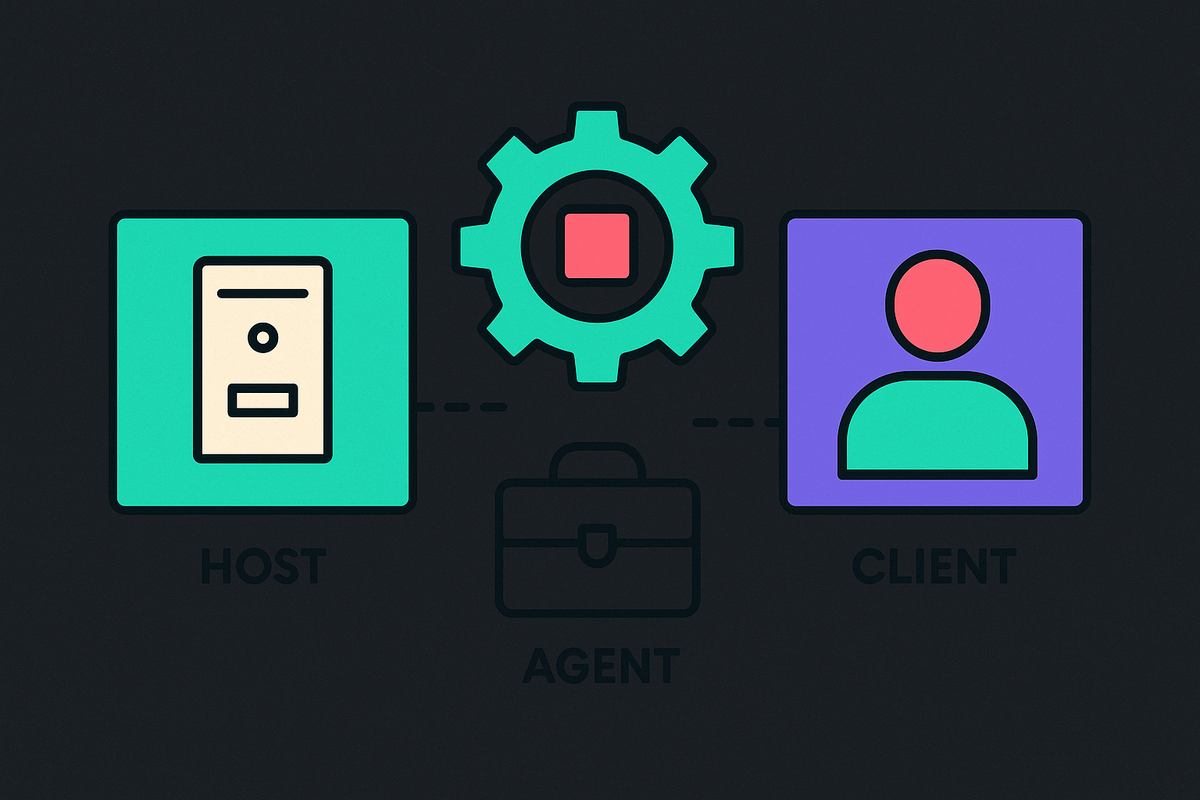
Mixing up host and client roles in MCP creates security gaps in production.
Start with read-only workflows to build confidence before expanding agent permissions.
Security and identity layers determine whether enterprise MCP deployments actually work at scale.
Orchestrated AI agents multiply security risks faster than enterprises can secure them.
Five MCP server categories now guide enterprise deployment decisions and governance rules.
When agents call tools wrong, downstream steps inherit fabricated data as fact.
Most enterprises are deploying AI agents without the security architecture to protect them.
Agentic AI systems break NIST's risk framework at every function.
JPMorgan and Morgan Stanley show how narrow, specialized agents tackle enterprise work at scale.
Enterprises must vet MCP servers before production use, not after adoption spreads.